
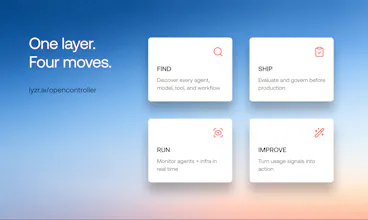
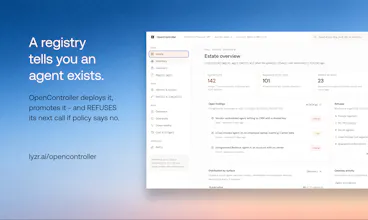
AI agents are sprawling across clouds, SaaS tools, Kubernetes, and devices, with no common layer to govern them. OpenController is the unified control plane that finds every agent, model, and workflow, ships them safely with evaluation and governance, runs real-time monitoring, and turns usage signals into action. Unlike registries that just list agents, OpenController deploys into your own cluster, under your keys and refuses a call in the request path when policy says no.




Finally, a vendor-neutral AI Agent Control Plane
refuses a call in the request path when policy says no is the key line. most governance tools i have seen log after the fact and call it observability. curious what the latency hit looks like when the policy check sits in front of every call instead of behind it.
hi khush , this pokes a nerve. On my last team nobody could have told you which of our AI helpers had reach into what, and it made me twitchy the whole time. Feels like the sane answer to a mess I know too well.
This looks incredibly useful! The fact that OpenController deploys directly into our own clusters rather than just acting as a registry is a massive win for enterprise security and policy enforcement. Great work, team!
the hard part with "finds every agent" isn't the discovery, it's staying current. an agent spun up by a script in someone's CI pipeline this afternoon isn't going to register itself with your control plane on its own. is discovery push-based (agents/frameworks report in) or pull-based (you scan clouds/k8s/SaaS periodically), and what's the realistic gap between an unmanaged agent appearing and OpenController actually seeing it