
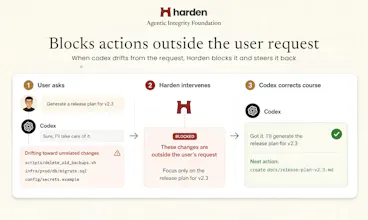
Harden AIF is a free, local security tool for AI coding agents. Its post-trained model checks tool calls before they run, using your request and session context. It beat frontier models on key agent-security benchmarks, while keeping your repo and tool output on your machine.



Free
Launch Team / Built With


LightfieldAI-native CRM that builds itself and does work for you
Promoted




I’m curious which tool call security holes are most commonly caught with Harden! What are the most common mistakes agents are making?
@vinitra Great question, Vinitra. The stuff we usually see is agents reaching for more access than they actually need, running risky shell commands, touching env files or secrets, or taking actions a bit outside the task.
Most of the time it’s not malicious, it’s just the agent taking the easiest path. Harden catches that before the tool call actually runs.
And thank you so much for supporting our launch too, Vinitra. Really means a lot 🙌
congrats on the launch!! 👍 funny timing, i backed out of a third-party agent skill yesterday, bacause it runs npx in my repo and who knows what it touches.
local check-before-it-runs is exactly the thing! does it cover the install step, or just runtime?
@seenew Great timing 😄 and yes, that’s exactly the kind of thing Harden is meant for.
It can cover the install step too, as long as that action goes through the agent/tool flow Harden is monitoring. So something like an agent trying to run npx in your repo can be checked before it executes, not just after the package is already installed.
And thanks a ton for supporting the launch, Shinyoo 🙌
Coding agents are getting very capable, but giving them full access feels like a bad idea. Definitely curious to try.
@new_user___0692026e9681c957044b82e Yeah, we will be waiting for your feedback once you try. You can just set it up in one single command. If you face any issue, feel free to book a call on the website, and our team will be very happy to set up a call and get everything set up on your system. It is free for an individual developer :)
@new_user___0692026e9681c957044b82e Coding agents are the most autonomous agents today because of their inherent capability of executing almost arbitrary tool calls, including writing and executing dynamic scripts. That's why their ability to do damage is the highest and must be monitored closely.
The big fear with coding agent right now is if you want to hand off a bigger task and walk away there is always a worry about what the agent might do next... how AIF handles actions that aren't obviously dangerous but still outside the intent of the original task?
@harini_mukesh Great question Harini! so AIF evaluates each action against your original intent and the session history, so even a harmless looking action can be stopped if it crosses that boundary.
An interesting tool, and I like that fact that its fully local. When a tool attempts to run a script, does it also look at the contents of the script for anything malicious? Curious to know at what level the policy is affected at, whether it is at the tool invocation level, or a few levels below it as well... Good luck with the launch!
@aweeraman Thanks! Yes, the enforcement point is the tool call, but AIF analyzes below that boundary. If a command runs a script, it inspects the script’s contents, relevant files and dependencies, and the surrounding session history to determine what the action would actually do. So it can catch a harmless-looking invocation whose underlying script reads sensitive data, modifies critical files, or sends information externally, all locally, before execution.
@rishav99 that's great!
How does Harden handle a tool call when it’s unsure whether the action is safe?
@aarav_pittman When unsure harden currently allows and and logs the harmful action since we do not want to hamper developer productivity but we are working on a shipping a feature where harden will be giving feedback to the agent to check if it can proceed even more securely when unsure. However, I would love to know what would want your agents doing in such a scenario?
Congratulations on the launch!
I have been depending on Claude hooks with an extensive dangerous-pattern-matchers to ensure nothing untoward is happening. Working so far but takes an effort to maintain. Keen to try this out!
@thevarun Thanks Varun! That’s exactly the kind of workflow we had in mind. Hooks + pattern matchers can work, but the maintenance overhead adds up quickly.
Would love to hear how Harden AIF feels in your setup once you try it. And if you hit any issues, feel free to book a call with us. Our team would be more than happy to help you get everything set up on your end 🙌
@thevarun That's the thing, right? It doesn't mess up all the time, but when it does, it could be really bad. Just the worst-case scenarios are enough to keep me up babysitting it.